


Important information:
Am 10. April 2024 wurden das Kundenportal sowie der Web-Zugriff auf das Kartenkonto eingestellt. Bitte laden Sie die Swiss Bankers App herunter, um weiterhin uneingeschränkten Zugriff auf alle Dienste zu haben.
Are you a Swiss Bankers sales partner?
Hier geht es zum Partnerportal.
A supposed parcel notification, a blocked card or an urgent payment request – at first glance, text messages like these often seem entirely credible. This is exactly what fraudsters are counting on: they want to trick you into clicking a link straight away so they can get hold of your personal details, passwords or credit card information. Find out how smishing works, what warning signs you should be aware of and how you can protect yourself effectively.
 03.10.2026
 Miryana
Smishing is a portmanteau of the terms ‘SMS’ and ‘phishing’. It involves fraudsters sending messages that appear trustworthy at first glance – for example, purporting to be from a bank, a parcel delivery service, a government agency or a mobile phone provider.
The aim is to get you to react as quickly as possible and disclose sensitive information – without realising that this information ends up directly in the hands of the fraudsters. Typical requests include:
to click on a link leading to a fake website,
to enter personal details, passwords or credit card details,
to install a malicious app,
to call back a phone number behind which fraudsters are hiding.
Smishing is a form of social engineering. Rather than exploiting technical vulnerabilities, the perpetrators specifically target human reactions – such as time pressure, fear, trust or curiosity.
Smishing exploits situations that are familiar to us from everyday life – and that is precisely what makes the scam so convincing.
High attention: Text messages are often read straight away. On our smartphones, we also tend to react more quickly than we do to check a message more carefully.
Fake senders: Sender names can be manipulated. This means a fraudulent message can appear to come from a well-known bank or company – and in some cases even appear in the same message thread as genuine text messages.
Small screen: Long web addresses are harder to check on a smartphone. This means suspicious links are less likely to be spotted straight away.
Relevance to everyday life: Parcels, bank accounts, bills or messages from public authorities affect almost everyone. That’s why such a text message often seems credible at exactly the right moment.
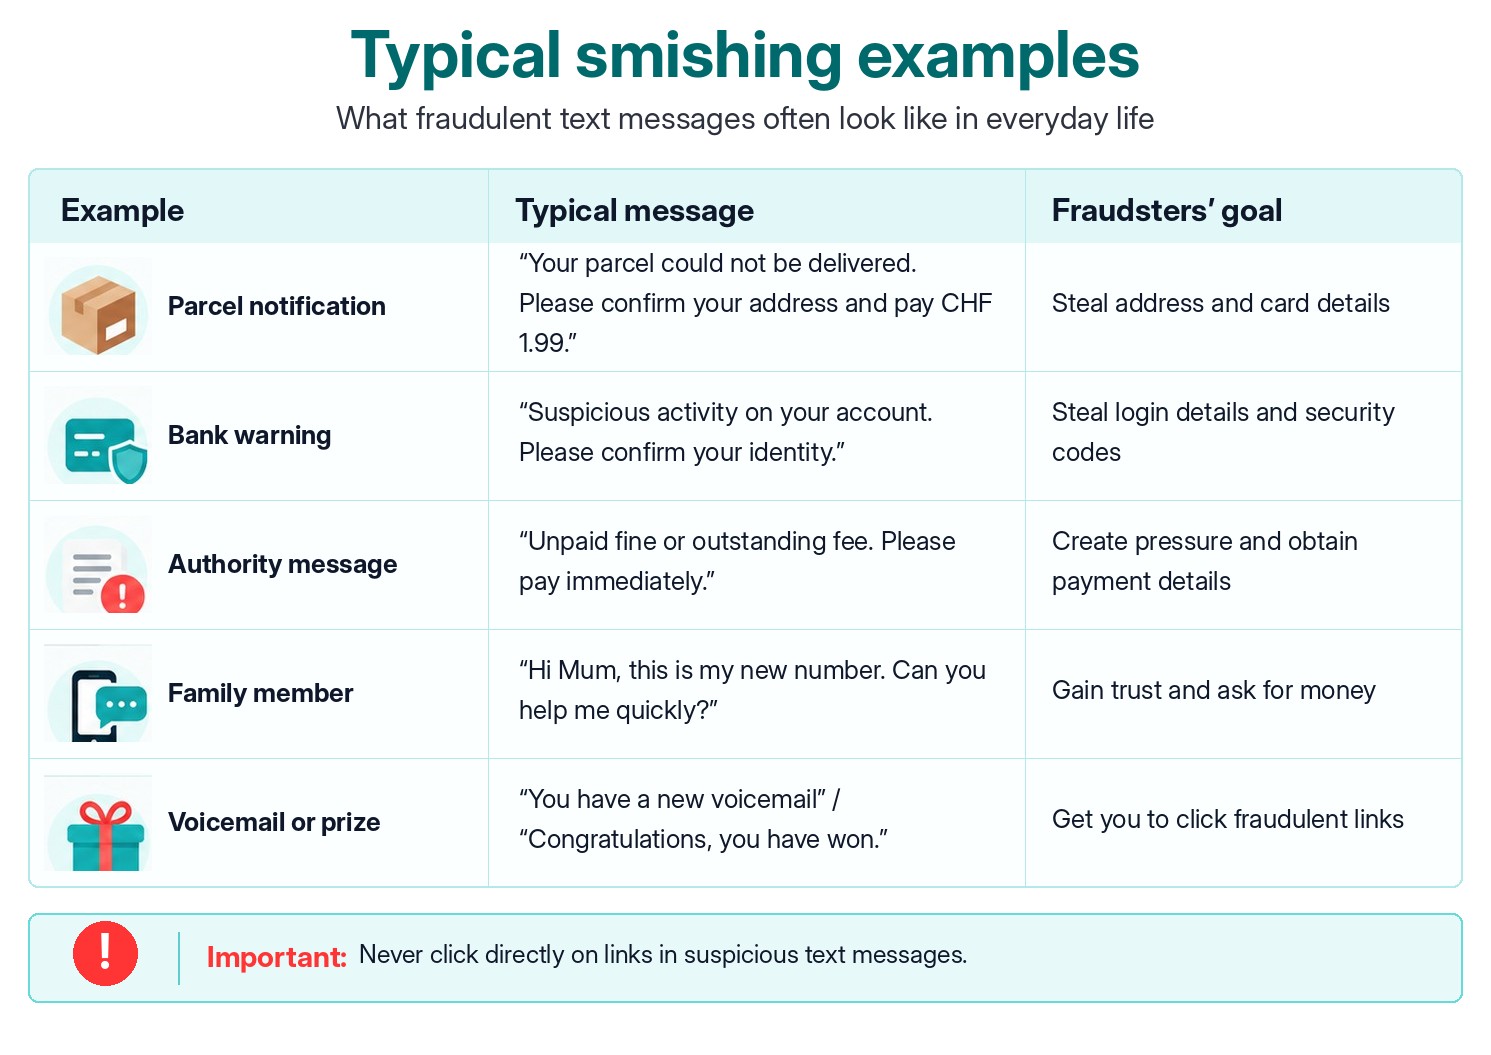
Smishing messages can take many different forms, but they usually follow the same principle: they appear familiar, create a sense of urgency or arouse curiosity, and are designed to trick you into reacting quickly. Fraudsters particularly often pose as parcel delivery services, banks, government agencies or even family members. The following overview shows typical examples from everyday life – and what the fraudsters are trying to achieve with them.
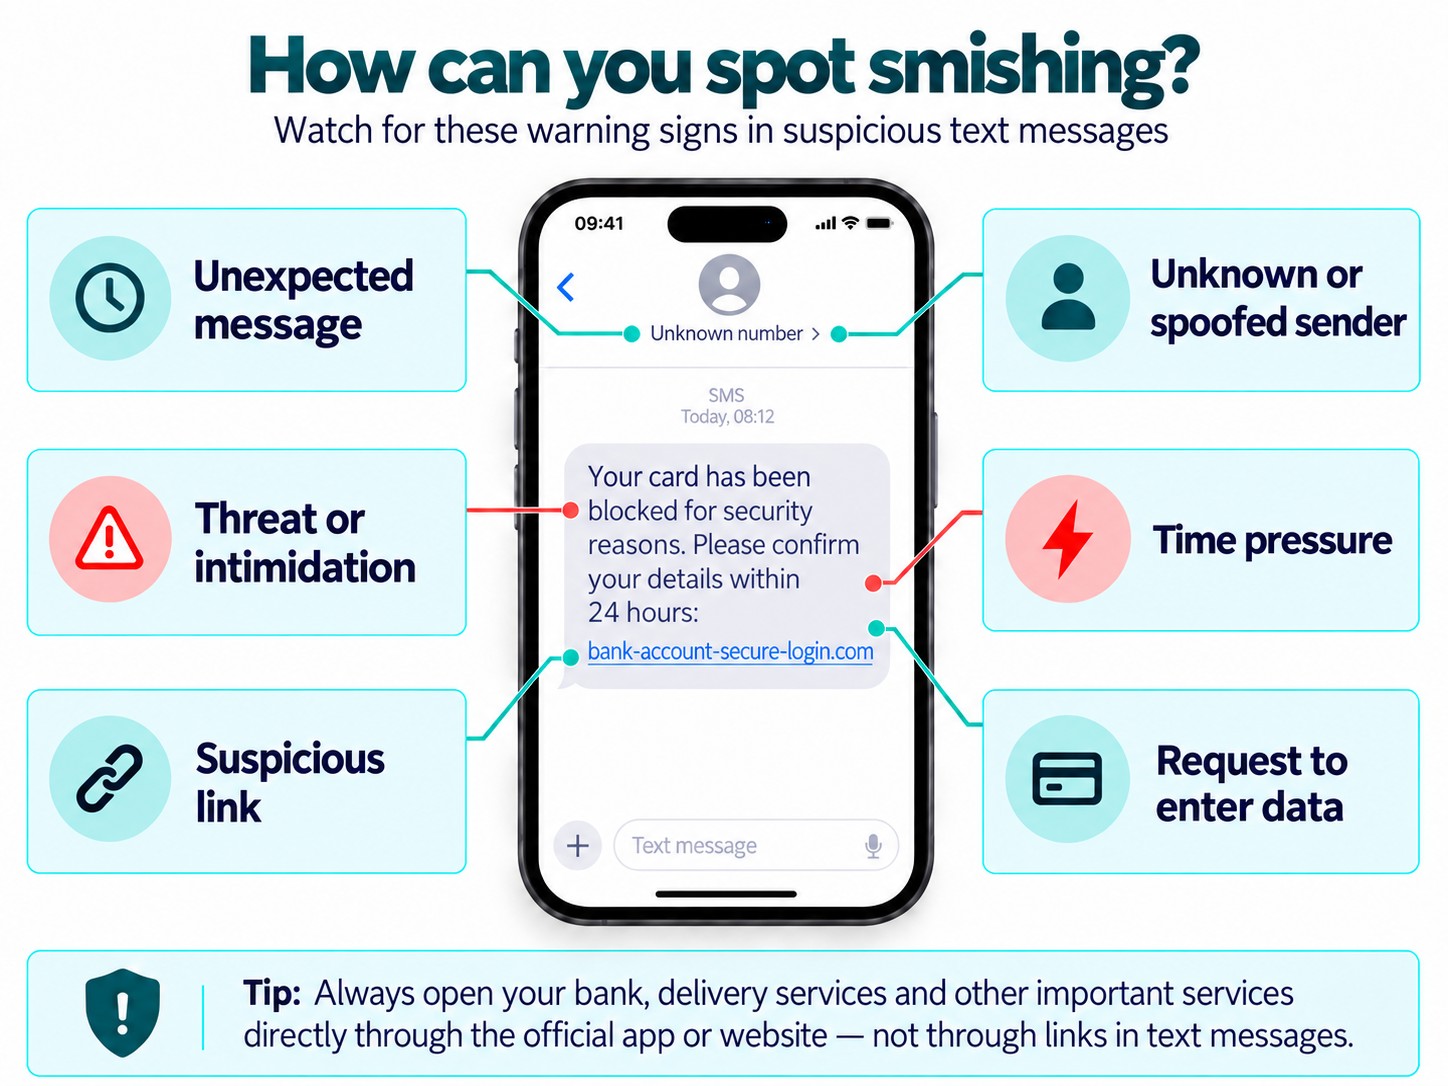
Even professionally crafted smishing messages often display typical warning signs:
Requests to enter personal details: Banks and reputable organisations will not ask you via text message to enter or disclose passwords, PINs or TANs via a link. If such details are requested, this is a clear warning sign.
Time pressure and threats: Phrases such as ‘within 24 hours’ or ‘your account will be blocked’ are designed to prompt a quick response from you.
Unexpected messages: For example, you might receive a parcel notification even though you are not expecting a delivery, or a message from a provider with whom you do not even have an account.
Fake sender: Sender names and telephone numbers can be manipulated. This means a fraudulent text message can appear to come from a well-known bank or company – sometimes even appearing in the same message thread as genuine texts.
Suspicious links: Watch out for unusual web addresses, typos, extra words or unusual domain extensions.
Requests to enter personal details: If you’re asked to enter passwords, PINs, security codes or credit card details via a link, you should be particularly cautious.
Impersonal or unusual form of address: General forms of address can be a warning sign – although modern scam messages sometimes also use names and personal details.
Linguistic anomalies: Spelling mistakes, unusual phrasing or special characters may indicate a scam. However, do not rely on this alone: many smishing messages are now written in a very professional style.
Important: A sender that appears familiar or a message free of errors does not automatically mean that the text message is genuine.
If a text message seems suspicious, there’s one thing you should do above all else: don’t react too hastily.
Do not click on any links in the message.
Do not reply and do not call back any number given in the message. Even a reply can show the perpetrators that your number is actively in use.
Do not enter any personal details, passwords or credit card information.
Verify the message independently: open the official app or website of the alleged sender yourself and check there to see if a message has actually been sent.
If you are unsure, contact the company using their official contact details.
Delete the message and block the sender if it is clearly a scam.
Report suspicious messages. You can report phishing and smishing attempts to the Federal Office for Cyber Security (BACS). This helps to identify fraudulent websites more quickly and enables appropriate measures to be taken.
It is important that you never use the link or contact details from the suspicious text message to verify anything. This will prevent you from being redirected directly to a fake website or to the fraudsters.
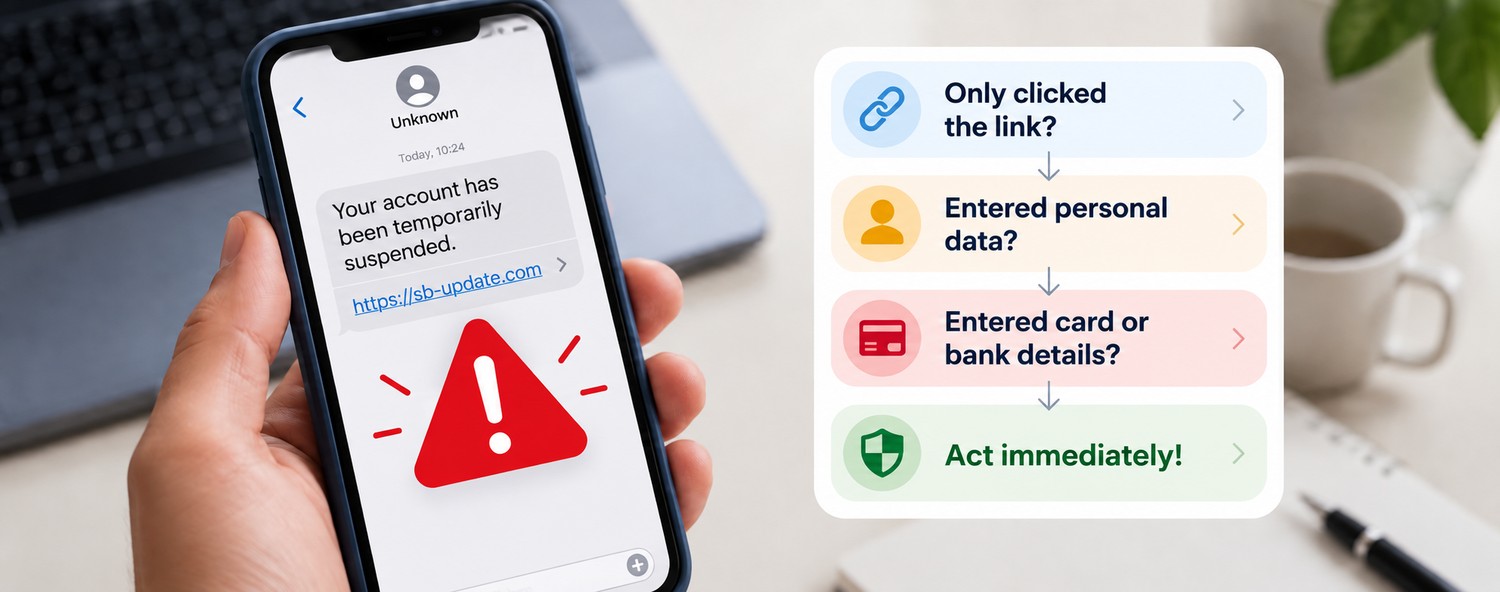
Clicking on a suspicious link does not automatically mean that any damage has already been done. What matters is what you did afterwards:
You’ve just clicked, but haven’t entered any details: Close the page and do not download any files or apps.
If you’ve entered your login details: Change the affected password immediately via the official website or app. If you use the same password for other services, you should change it there too. Enable two-factor authentication if possible.
If you entered bank or card details: Contact your bank or card provider straight away and check your transactions. If you have a Swiss Bankers card, you can use the ‘Replace card’ self-service option directly in the app if you suspect fraud.
Security codes disclosed: Contact your bank or card provider immediately. Such codes can enable fraudsters to confirm payments or logins.
An unknown app has been installed: First, disconnect your smartphone from the internet and remove the suspicious app. Also check its permissions. If you are unsure, have the device checked by a specialist and change important passwords from a trusted device.
You can report suspicious phishing links to the Federal Office for Cyber Security (BACS) via antiphishing.ch. If you would like to receive a response, please use the BACS online reporting form.
If you have already suffered financial loss, the BACS also recommends filing a criminal complaint with your local police. Keep the text message and, if possible, screenshots, telephone numbers, links and any other information relating to the fraud attempt.
As well as exercising caution when dealing with suspicious messages, certain settings can offer additional protection:
Enable two-factor authentication: this means that a stolen password alone is usually not enough to gain access to an account.
Check authorisations carefully: Only confirm TANs, security codes or requests in banking apps if you have initiated the transaction yourself.
Keep your smartphone and apps up to date: Regular updates patch known security vulnerabilities.
Only install apps from official stores: Where possible, disable the option to install from unknown sources.
Use spam and message filters: Many smartphones and mobile network providers can automatically detect suspicious text messages or filter out messages from unknown senders.
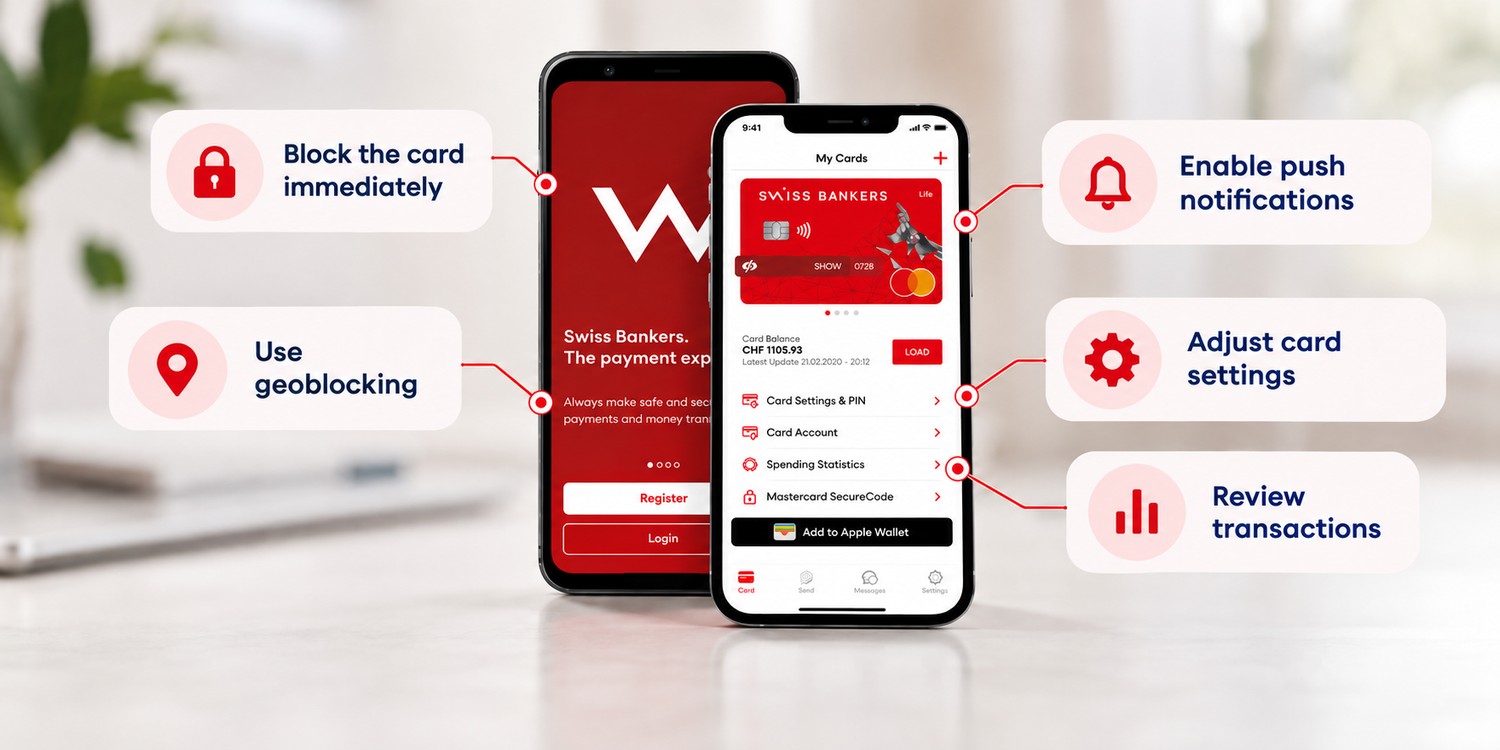
Enable transaction notifications: Push notifications help you spot unfamiliar card transactions quickly.
With the Swiss Bankers app, you can keep track of your card activity and manage various security settings directly. Push notifications inform you about transactions and help you spot unusual card activity at an early stage. If necessary, you can block and unblock your card directly in the app, as well as use geoblocking to block payments in specific regions.
Smishing messages often appear deceptively genuine and deliberately exploit time pressure, trust or curiosity. This makes it all the more important to remain vigilant when receiving unexpected text messages and not to click on links too hastily. Always verify suspicious requests via the provider’s official app, website or helpline. If you have already entered details or confirmed a payment, you should act quickly and contact your bank or card provider.
Also talk to family members about current scams – particularly with older relatives or people who are less familiar with digital forms of fraud. Even a brief reminder can help them spot suspicious messages more quickly.

© Swiss Bankers 2026


 Compare cards and conditions

